Applied AI Security for Higher Ed Professionals: October 2026
Higher education institutions are rapidly deploying AI systems that handle sensitive student data. However, most security teams have never tested them for vulnerabilities. This hands-on Learning Lab equips higher education security professionals with practical skills to assess, defend, and govern AI systems.
Participants execute real attacks against large language models in a controlled cyber range built around higher education scenarios—performing prompt injection, extracting data from RAG systems, and bypassing safety controls. They then implement the defenses that stop these attacks: input validation, output filtering, guardrails, and detection systems.
The lab series concludes with governance integration, mapping technical skills to the NICE Framework AI Security Competency Area (NF-COM-002) for documented workforce outcomes.
Learning Outcomes:
NOTE: You will be asked to complete assignments in between the Learning Lab segments that support the learning outcomes stated below. You will receive feedback and constructive critique from course facilitators.
- Identify how common AI vulnerabilities manifest in higher education contexts such as chatbots, advising tools, and research assistants.
- Execute hands-on attack techniques to understand how adversaries exploit institutional AI systems.
- Apply defensive controls, including input validation, output filtering, and guardrails to protect AI deployments.
- Develop monitoring approaches to detect suspicious AI system behavior and potential misuse.
- Connect technical AI security skills to the NICE Framework for workforce development and documentation.
- Create a repeatable assessment process for evaluating AI systems across your institution.
Speaker Details
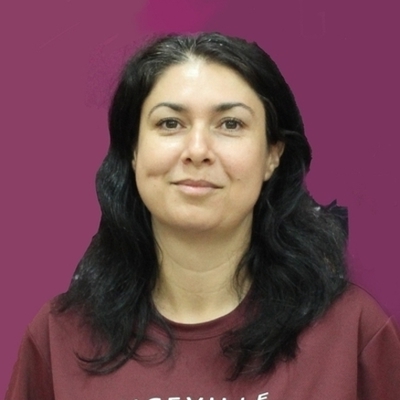
Iva Amos
Event Topic
Artificial Intelligence, K-12 / Higher Education, SecurityRelevant Audiences
All Education
Educause Members:
$ 360.00
Non-Member:
$ 465.00