Strengthening Open-Source Security Across the State of Texas
Engineering teams across Texas State agencies rely on diverse open-source ecosystems like Spring, Java, Python, Node.js, PostgreSQL and MySQL, which means keeping your software supply chain secure has never been more challenging.
Join us and your agency peers to learn more about how TrueSource by Broadcom can help your security teams tackle open-source risk head-on through:
- Unified Ecosystem Coverage: Secure, curated remediation across Spring, Python, Node.js and critical data engines like PostgreSQL, MySQL, Valkey and RabbitMQ.
- Human-Verified Remediation: Prioritize engineer-led verification over fully automated AI-patching to prevent application breakage.
- Verifiable Supply Chain Integrity: All artifacts are delivered at supply-chain levels for software artifacts (SLSA) Build Level 3, eliminating transitive dependency risks.
- Open-Source Commitment: We contribute fixes upstream, actively supporting the health of the communities we rely on.
- Advanced Spring Automation: Automated repository scanning, blast-radius assessment and proactive pull-request generation.
- Enhanced Spring Support: Early access to common vulnerabilities and exposures (CVE) and patching for current and long-term support (LTS) versions (before open-source software availability) and 24x7 support from the sole engineering team contributing to Spring Enterprise.
Over 97% of enterprise applications rely on open-source software components. Join this session to discover how TrueSource by Broadcom can help you stay proactive in the face of emerging open-source risks.
Speaker Details
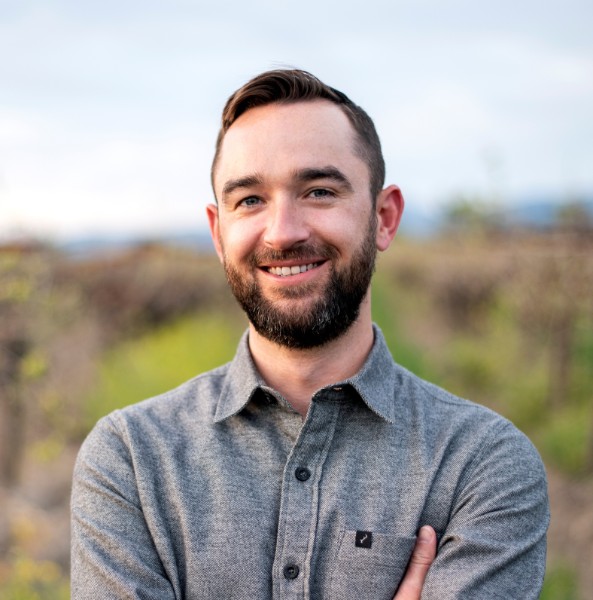
Ryan Conley
Global Field Principal
Broadcom
Derek Beauregard
Tanzu Solutions Architecture
Broadcom
Event Topic
Open Source/OSINT, Risk Management/RegulatoryRelevant Audiences
All State and Local Government
Event Type
Virtual / Online
Event Subtype
Webinar / Webcast
When
Wed, Nov 18, 2026 | 2:00 pm - 3:00 pm CT
Registration Cost
Complimentary
Sponsor
Organizer