Wiz
Events We Are Sponsoring
According to Mandiant’s M-Trends 2026 report, exploits remain one of the most common entry points for adversaries, while attackers are increasingly targeting edge and core network devices. These devices can create significant blind spots because they often cannot support traditional endpoint security tools, giving threat actors an opportunity to establish persistence and move deeper into an environment. Join your Bay Area public sector peers and security leadership for an exclusive, in-person discussion focused on information sharing and collaborative defense. Together, we'll explore how today's sophisticated threat actors target interconnected infrastructure from cloud and IT environments down to edge devices, OT and IoT — and how local teams can coordinate to close the gaps across our regional landscape.
|
All of DFIR. One Event.
Digital Forensics | Incident Response | Ransomware | Threat Hunting
The SANS DFIR Summit & Training is back—in a new city, a new season, and with our most in-depth program yet.
This year, the Summit has expanded to tackle today’s most challenging DFIR topics—from core digital forensics and incident response to focused deep dives in threat hunting and ransomware—through expert-led talks, open-source tool sessions, and more hands-on opportunities than ever before.
If staying sharp on the latest research, tools, and investigative tradecraft matters to you, this is where you need to be.
Summit: Oct 15-16 | Training: Oct 17-22
SANS 2026 DFIR Summit Solutions Track delivers a deep technical exploration of the tools, methodologies, and operational models driving next-generation digital forensics and incident response. Sessions focus on advanced evidence acquisition, host and network artifact analysis, memory forensics, cloud-native IR workflows, and the application of machine learning to accelerate triage and attribution.
Attendees will learn how to operationalize automation, standardize investigative pipelines, and integrate DFIR technologies into high-scale, distributed environments to improve precision, reduce dwell time, and harden enterprise response capabilities.
What to Expect
- Technical walkthroughs of emerging DFIR tooling—including endpoint telemetry pipelines, memory forensics frameworks, malware analysis sandboxes, and automated evidence extraction workflows.
- Deep-dive case studies detailing attacker tradecraft, artifact correlation strategies, cross-host timeline reconstruction, and cloud IR techniques across AWS, Azure, and GCP.
- Practical guidance and reference architectures for building scalable DFIR environments with automated triage, standardized enrichment, and integrated SOAR/EDR workflows.
Who Should Attend
- DFIR practitioners, digital forensic examiners, threat hunters, and reverse engineers seeking advanced, tool-focused investigative techniques.
- Incident response leads and SOC engineers responsible for building automated triage pipelines, forensic readiness strategies, and high-throughput investigation environments.
- Security architects and platform engineers integrating DFIR telemetry, EDR/XDR data, and cloud-native artifacts into centralized analysis and response systems.
- Organizations evaluating next-gen DFIR platforms, scaling IR operations, or adopting automation and ML-driven investigative workflows.
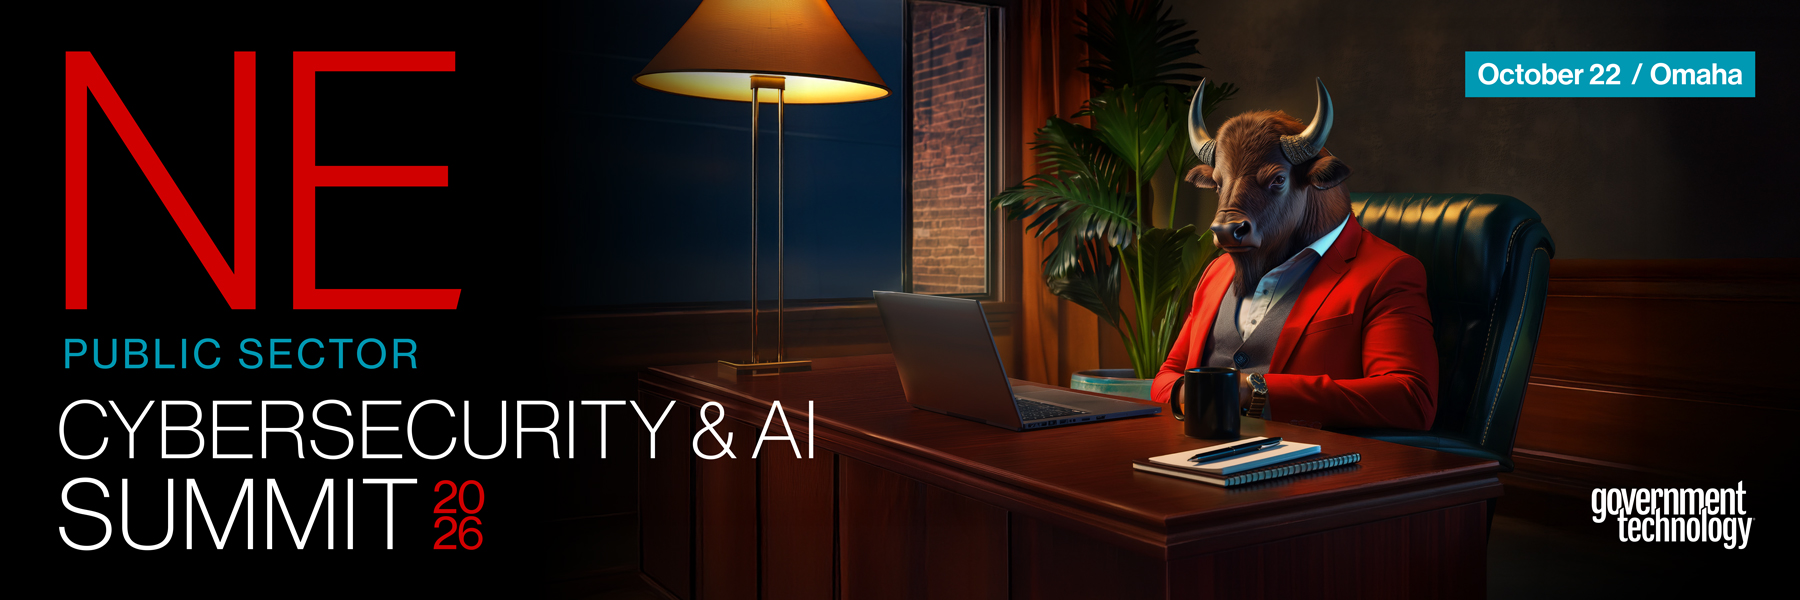
The Nebraska Public Sector Cybersecurity & AI Summit is where government defends the future.
This public sector-focused event brings together IT security leaders, risk managers, and public officials to tackle the evolving cyber threats facing state and local government. Through expert-led sessions, peer exchange, and real-world case studies, attendees gain practical strategies to strengthen cyber resilience, protect critical infrastructure, and lead with confidence in an age of constant risk. Designed specifically for the public sector, this summit delivers insights you can act on and alliances you can trust!
This is a hands-on, technical-focused, executive-centric immersive experience across three distinct tracks:
Practitioner Track
A Capture the Flag competition calibrated for participants with hands-on technical experience, competing solo or in teams of two. Under real-time pressure, secure a live environment, protect critical assets, and get ahead of cloud, data, and cryptographic risk using industry-leading technologies to capture each prized digital flag.
Limited seats available.
Executive Track
An interactive Tabletop exercise and intimate roundtable discussions designed for CISOs, CIOs, and senior executive leaders. Hear directly from top voices across federal, SLED, and industry shaping the future of cyber resilience.
General Audience Track
No hands-on component required. Attend the Keynote lunch and panel discussions, explore partner exhibits with the latest innovations, and network at your own pace.
In the rush to innovate, well-intentioned employees may deploy DIY chatbots and generative AI tools. While these tools promise efficiency, they can expose public sector organizations to significant data leakage and compliance risks.
Join Google Public Sector, SHI and Wiz for a critical look at how AI emerges in government environments, illustrated by real-world incidents such as city staff pasting sensitive resident data into chatbots and breaches caused by agentic AI with unchecked access. Our experts will break down the hidden dangers of AI, and show you how to protect your agency with secure development practices, robust access controls, and comprehensive AI governance frameworks.
Key Takeaways:
- Real examples of AI-driven data leaks and breaches in the public sector
- How to detect and mitigate risks from AI and chatbots
- Best practices for secure AI development and deployment
- Building effective access controls and governance with SHI, Google, and Wiz
- Q&A with security and AI governance experts
The SANS Fall Cyber Solutions Fest 2026: Identity Security and Zero Trust Track delivers a deep technical examination of identity as the modern attack surface. As adversaries exploit misconfigured IdPs, weak federation trust, poisoned authentication flows, and over-permissioned service principals, this track analyzes the mechanics of identity compromise across multiple attack surfaces, and hybrid environments. Sessions will dissect novel identity threat vectors, including token replay and manipulation, MFA fatigue attacks, conditional access bypass techniques, and identity infrastructure persistence. Practitioners will gain prescriptive guidance on securing authentication pipelines, hardening federation architectures, and monitoring high-risk identity events with advanced telemetry.
Anchored in Zero Trust architecture, the track focuses on continuous policy enforcement, adaptive authentication, micro-segmentation, and automated privilege reduction across distributed systems. Experts will present reference architectures and implementation patterns for identity-centric Zero Trust deployments, covering identity threat detection and response (ITDR), identity-driven segmentation, policy decision point/orchestration design, and integration of identity context into SIEM, XDR, and SOAR workflows. Attendees will leave with actionable techniques for securing machine identities, enforcing least privilege at scale, validating trust signals in real time, and operationalizing Zero Trust across multi-cloud and SaaS ecosystems.
Events Where We Are Exhibiting
The New York City Public Sector Cybersecurity Summit is where government defends the future.
This public sector-focused event brings together IT security leaders, risk managers, and public officials to tackle the evolving cyber threats facing state and local government. Through expert-led sessions, peer exchange, and real-world case studies, attendees gain practical strategies to strengthen cyber resilience, protect critical infrastructure, and lead with confidence in an age of constant risk. Designed specifically for the public sector, this summit delivers insights you can act on and alliances you can trust!
Open to Public Sector only.